

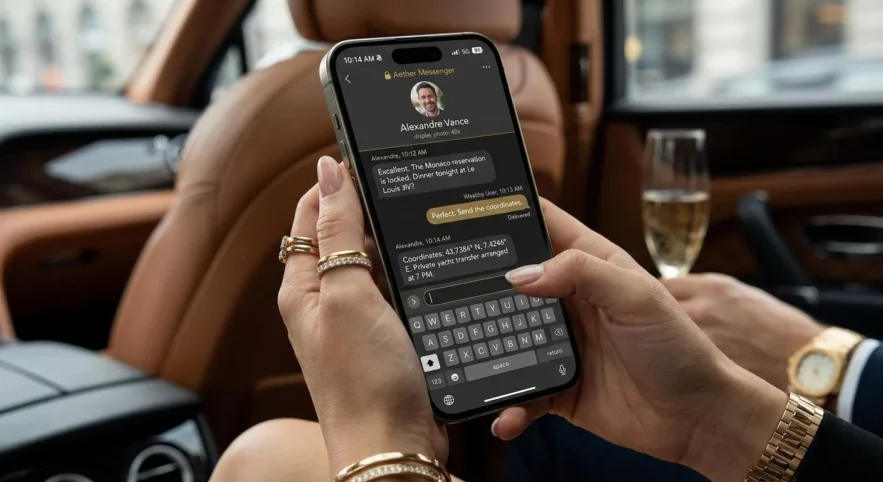
Managing access to itineraries and personal documents requires more than choosing a messaging platform, especially when multiple organizations coordinate the same journey and sensitive information must remain protected across international transportation, hospitality, financial, and professional service networks.
WASHINGTON, DC, October 28, 2026: Secure communications have become essential to confidential international travel planning as business executives, public figures, prominent families, and privacy-conscious travelers increasingly rely on multiple service providers to coordinate transportation, accommodation, identification documents, and overseas appointments.
Although encrypted messaging apps and specialized email platforms can better protect sensitive communications, their effectiveness depends on broader security arrangements governing who receives information, how documents are stored, and whether participating organizations maintain appropriate access controls.
The growing complexity of international travel arrangements means a single itinerary may be shared among airlines, charter operators, hotel managers, private transportation companies, security consultants, and local representatives, each potentially using different information-security practices.
For travelers seeking discretion, the key consideration is not simply whether a messaging app provides encryption, but whether every organization involved handles confidential information responsibly throughout the reservation, travel, and post-departure process.
Confidential Travel Planning Begins With Information Control
An international journey can generate extensive personal information before departure, including passport details, travel dates, accommodation addresses, payment records, emergency contacts, and confidential professional schedules that may be required by several organizations delivering different services.
When these details circulate without clear restrictions, the number of employees, contractors, and technology providers who can access sensitive information can increase significantly, even when the original travel adviser maintains appropriate confidentiality procedures.
Effective information control starts with identifying which details each service provider genuinely needs and establishing procedures that limit additional disclosure without compromising legitimate transportation, accommodation, safety, or government identification responsibilities.
For example, a chauffeur may need accurate pickup instructions and relevant contact information but ordinarily does not need unrestricted access to a client’s financial documents, confidential business correspondence, or full international travel history.
Encrypted Messaging Is Only One Part of Communication Security
End-to-end encryption can protect message contents against interception while information travels between appropriately configured communication endpoints, making it an important security consideration for advisers and travelers exchanging sensitive material during international preparations.
However, encryption does not necessarily prevent an authorized recipient from forwarding information, taking screenshots, saving documents outside a protected application, or exposing confidential material through a compromised personal computer or mobile device.
Communication security must therefore include device protection, appropriate authentication, recipient verification, employee training, and carefully managed permissions, rather than relying exclusively on the technical features advertised by an individual messaging service.
Organizations should also consider whether cloud backups, linked devices, account recovery methods, and retained downloaded attachments introduce additional risks that require safeguards beyond those protecting messages in transit.
Cybersecurity Concerns Have Reached Major Travel Platforms
The link between travel reservations and digital security drew renewed scrutiny in October 2026, when European regulators began examining concerns about fraudulent accommodation listings, impersonation attempts, and phishing activity linked to a major international booking platform.
On October 21, 2026, Reuters reported that the European Commission is investigating Booking.com over regulatory concerns about fraudulent listings and phishing schemes that may exploit reservation information shared with accommodation providers.
The investigation does not establish that all travel booking systems are insecure, but it highlights how criminals may exploit trusted commercial relationships and genuine reservation details to make fraudulent communications appear credible to unsuspecting travelers.
For clients organizing confidential journeys, these developments reinforce the importance of independently verifying unexpected requests involving payments, identity documents, account credentials, or changes to previously confirmed arrangements before responding or transferring sensitive information.
Passport Copies Require Stronger Document Handling Procedures
Passport scans and other identification documents contain personal details that can become valuable to identity thieves when transmitted through insecure channels, retained unnecessarily, or distributed among organizations without appropriate access restrictions.
Travel advisers may legitimately require travel-document information to arrange reservations, while airlines, immigration authorities, and certain accommodation operators may collect additional identification details under applicable laws and established administrative procedures.
These legitimate requirements do not justify unrestricted copying or storage, so professional travel coordinators should confirm why documents are requested, which organization will receive them, and how the information will be protected.
When organizations must transmit identification records electronically, they should use secure document-transfer methods, restrict access appropriately, and establish clear retention procedures that distinguish lawful recordkeeping from unnecessary preservation of sensitive personal information.
Email Security Requires More Than a Confidentiality Disclaimer
Electronic mail remains widely used for booking confirmations, contracts, invoices, and travel documentation, but typical email arrangements may involve multiple servers, cloud storage systems, archived attachments, and recipients with different security practices.
A confidentiality statement at the bottom of an email can communicate expectations about the intended audience, yet it does not technically prevent unauthorized access, accidental forwarding, account compromise, or inappropriate retention.
For particularly sensitive international arrangements, secure email services, properly configured encryption, and verified recipient addresses can offer additional protections when combined with disciplined document management and organizational information-security procedures.
The reliability of these safeguards depends on both the sender and recipient, because even a securely transmitted document can become exposed when downloaded onto an unprotected device or forwarded outside the authorized communication group.
Multi-Factor Authentication Protects Access to Travel Accounts
Travel planning commonly involves access to email accounts, shared document repositories, airline profiles, booking platforms, and payment systems, creating multiple opportunities for unauthorized individuals to obtain sensitive information through compromised credentials.
Multi-factor authentication adds an extra layer of protection by requiring users to prove more than a password, reducing the likelihood that stolen login credentials alone will grant unauthorized account access.
Organizations handling confidential itineraries should apply appropriate authentication controls to administrative accounts, document storage systems, and communication platforms, paying particular attention to employees who manage identification records or sensitive financial information.
The strongest arrangements also establish clear procedures for recovering compromised accounts, withdrawing access when personnel leave an assignment, and verifying unusual requests that appear to originate from trusted colleagues or business partners.
Shared Travel Itineraries Should Have Defined Access Permissions
Complex international journeys often require multiple organizations to consult shared travel schedules, accommodation confirmations, passenger information, and transportation arrangements, creating practical reasons to use shared digital itineraries or centralized coordination platforms.
Without carefully configured permissions, however, employees with relatively narrow tasks may gain access to unrelated personal information, including private meeting schedules, identification documents, and details about family members accompanying an executive.
Access controls should therefore reflect specific professional responsibilities, allowing each provider to view the information required for its assigned services while restricting unrelated material that does not support a legitimate operational purpose.
A useful system should also support timely updates, controlled document sharing, and permission removal when assignments conclude, reducing the chance that former contractors can still access historical travel information.
Government Guidance Emphasizes Data Security Across Organizations
Protecting confidential travel information reflects broader cybersecurity principles that apply to businesses handling sensitive customer records, especially when external contractors and digital service providers participate in normal commercial operations.
The Federal Trade Commission’s guidance on protecting personal information advises organizations to understand the information they hold, limit unnecessary collection, protect stored records, and establish appropriate procedures for managing access and responding to security incidents.
These principles matter especially for international travel coordination because identifying information may pass through several independent businesses, creating risks that examining the original travel agency alone cannot adequately address.
Organizations managing confidential journeys should understand their suppliers’ responsibilities, set clear security expectations, and verify that subcontractors handling sensitive data maintain safeguards appropriate to their assignments.
Travel Security Depends on Verifying Communication Recipients
One of the most common weaknesses in confidential travel coordination occurs when an employee sends sensitive documents to the wrong person, relies on outdated contact information, or accepts an unexpected request from someone impersonating a legitimate service provider.
Fraudulent messages may seem convincing when they reference real hotel reservations, flight schedules, payment amounts, or client names, so independent verification is especially important when a communication requests additional documents or changes to established financial instructions.
Professional advisers should maintain reliable contact records, establish procedures to confirm unfamiliar requests, and ensure employees know when to withhold sensitive information until they confirm the recipient’s authority.
These protections should remain proportionate to the information involved, allowing ordinary logistical communications to proceed efficiently while applying greater scrutiny to passport copies, banking records, confidential itineraries, and other sensitive materials.
Local Transport Providers Need Limited but Accurate Information
Ground transportation companies often require passenger names, pickup locations, flight arrival details, contact numbers, and destination addresses to coordinate reliable service, particularly when international travelers arrive at unfamiliar airports or transportation facilities.
However, transportation employees rarely need unrestricted access to detailed professional schedules, personal financial records, unrelated passport copies, or confidential discussions occurring between travelers and their international business advisers.
A centralized travel coordinator can limit unnecessary disclosure by communicating relevant instructions directly to authorized dispatch personnel while keeping more sensitive material in appropriately secured administrative systems.
This approach supports legitimate confidentiality without compromising transportation safety because drivers and operational supervisors still receive the accurate information they need to identify passengers, manage schedules, and respond effectively to unexpected developments.
Hotels and Private Residences Introduce Separate Communication Networks
Accommodation arrangements may involve booking departments, reception staff, property managers, housekeeping supervisors, security personnel, and independent contractors who collectively require selected information to prepare guest rooms and coordinate requested services.
An exclusive hotel reservation or private villa booking can reduce public encounters, but it does not automatically prevent guest information from circulating through internal management software or communications between outside service providers.
Travelers should examine whether accommodation operators maintain controlled staff access, appropriate policies concerning confidential guests, and procedures that limit unnecessary circulation of personal documents or commercially sensitive travel schedules.
These safeguards matter most when private residences rely on temporary personnel or independent managers, because the parties responsible for delivering accommodation services may lack the centralized oversight of larger hospitality organizations.
Private Aviation and Yacht Charters Require Coordinated Documentation
Private aircraft and luxury yacht arrangements can offer considerable discretion during travel, but they still require passenger identification, safety documentation, financial records, and reporting to relevant aviation or maritime authorities.
Charter brokers, aircraft operators, vessel managers, crew members, and destination agents may receive different categories of information, making it important to distinguish legitimate operational access from unnecessary sharing across the wider service network.
Secure communications can help protect sensitive passenger records during coordination, but they cannot prevent mandatory declarations, conceal actual travelers from competent authorities, or substitute inaccurate identification information.
Responsible charter planning combines confidential commercial arrangements with accurate documentation and appropriately restricted access to information, ensuring travelers receive professional service while operators meet their legal and safety responsibilities.
Anonymous Travel Planning Requires Lawful Confidentiality
Privacy-conscious international travelers may seek to reduce unnecessary exposure of their identities, itineraries, accommodation preferences, and professional activities, particularly when their circumstances create legitimate concerns about personal safety or unwanted public attention.
Amicus International Consulting addresses these considerations through anonymous travel advisory services focused on discreet international mobility, confidential planning, and the practical relationship between personal privacy and lawful travel documentation.
Within this framework, secure communications support legitimate confidentiality by protecting information from unauthorized commercial or public disclosure, rather than helping travelers avoid immigration procedures or mandatory identification requirements.
Travelers can therefore seek appropriate restrictions on commercial information sharing while continuing to provide accurate passport details, comply with government reporting obligations, and maintain legitimate records required by transportation and accommodation providers.
Confidentiality Agreements Should Include Communication Responsibilities
Non-disclosure agreements can protect sensitive travel arrangements, but their practical value depends on whether obligations extend to authorized employees, outside consultants, subcontractors, and organizations receiving confidential information.
An effective agreement should address permitted communications, protection of identifying details, restrictions on unauthorized publication, information-retention responsibilities, and procedures for responding when an employee or contractor suspects that sensitive records have been improperly disclosed.
Contractual language should also set out realistic exceptions for lawful reporting, emergency assistance, and valid governmental information requests, ensuring confidentiality arrangements do not conflict with applicable legal requirements.
For complex international journeys, advisers and clients may benefit from legal review of confidentiality provisions, particularly when participating organizations operate in countries with different privacy legislation, contractual standards, and regulatory obligations.
Secure File Storage Matters After Documents Are Received
Electronic documents are not secure merely because they arrive through an encrypted communication channel, since recipients may download attachments, create local copies, forward files internally, or store sensitive material in shared systems.
Professional advisers should establish controlled storage arrangements, apply encryption where warranted, set individual user permissions, and document procedures for handling copies of passports, financial documents, client correspondence, and confidential travel schedules.
Organizations should also determine whether personnel may store information on personal devices, removable storage media, or unauthorized cloud accounts, because inconsistent practices can undermine otherwise strong communication protections.
Reliable document management requires ongoing oversight, not a one-time technical decision, to keep systems protected as employees change responsibilities, service providers complete assignments, and new travel arrangements add records.
Information Retention Extends Beyond the End of the Journey
International travel providers may retain reservation confirmations, invoices, identity records, communications, payment documentation, and operational reports after the traveler returns home, depending on applicable laws and the organization’s legitimate business requirements.
Some information must remain available for taxation, financial compliance, insurance administration, immigration records, or contractual disputes, while other material may no longer require storage once the original commercial purpose has ended.
Privacy-conscious clients should request clear explanations of relevant retention policies and available data-protection rights, recognizing that legitimate deletion requests may remain subject to mandatory legal or regulatory exceptions.
An appropriate information-management program should also identify outdated records, restrict access to retained files, and establish secure disposal procedures, reducing the unnecessary accumulation of personal information across successive international journeys.
Incident Response Procedures Protect Travelers When Problems Occur
Even carefully designed security arrangements cannot guarantee that every communication will remain confidential, making incident response planning essential when personal documents are misdirected, electronic accounts are compromised, or sensitive itinerary details reach unauthorized recipients.
Travel organizations should establish procedures to promptly identify suspected incidents, secure affected accounts, preserve relevant evidence, notify responsible personnel, and determine whether applicable laws require notifying affected customers or public authorities.
Clients should know whom to contact when a suspicious message appears, a document is sent in error, or someone claiming to represent a trusted provider unexpectedly requests personal information.
Prompt communication and clearly assigned responsibilities can reduce confusion during a security incident, allowing the participating organizations to coordinate legitimate protective measures without making unsupported assumptions about the nature or extent of the exposure.
International Travel Privacy Requires Consistent Professional Standards
Confidential travel planning becomes more challenging when service providers operate across national borders, since information may move between jurisdictions with different privacy laws, cybersecurity expectations, contractual obligations, and administrative procedures.
Travel advisers should understand these differences and establish suitable arrangements before transmitting sensitive records internationally, particularly when outside contractors process identification details, financial information, or confidential professional itineraries.
For travelers evaluating broader mobility and confidentiality requirements, Amicus International Consulting also describes its international privacy and consulting services, encompassing several advisory areas relevant to individuals considering overseas travel and related arrangements.
A coordinated approach to international privacy should combine accurate documentation, appropriate technical safeguards, qualified service providers, and clearly assigned information-handling responsibilities without suggesting that confidentiality eliminates legitimate governmental or financial oversight.
The Future of Confidential Travel Depends on Secure Coordination
As international transportation, hospitality, and professional services become increasingly interconnected, travelers will need to evaluate information security across the entire commercial network rather than relying exclusively on one messaging application’s security features.
Organizations that manage confidential travel should recognize that technical encryption, appropriate authentication, controlled document storage, contractual responsibilities, and employee training must work together to meaningfully protect sensitive personal information.
For executives, prominent families, and privacy-conscious individuals, the strongest arrangements combine professional discretion with accurate identity records, legitimate government compliance, transparent service-provider relationships, and carefully managed communications.
Ultimately, secure communications support confidential travel planning most effectively when every organization involved understands what information it may access, how it must protect that information, and when legitimate operational or legal responsibilities require carefully controlled disclosure.